ChatGPT Wallet Supports Agent Payments at Existing Checkouts
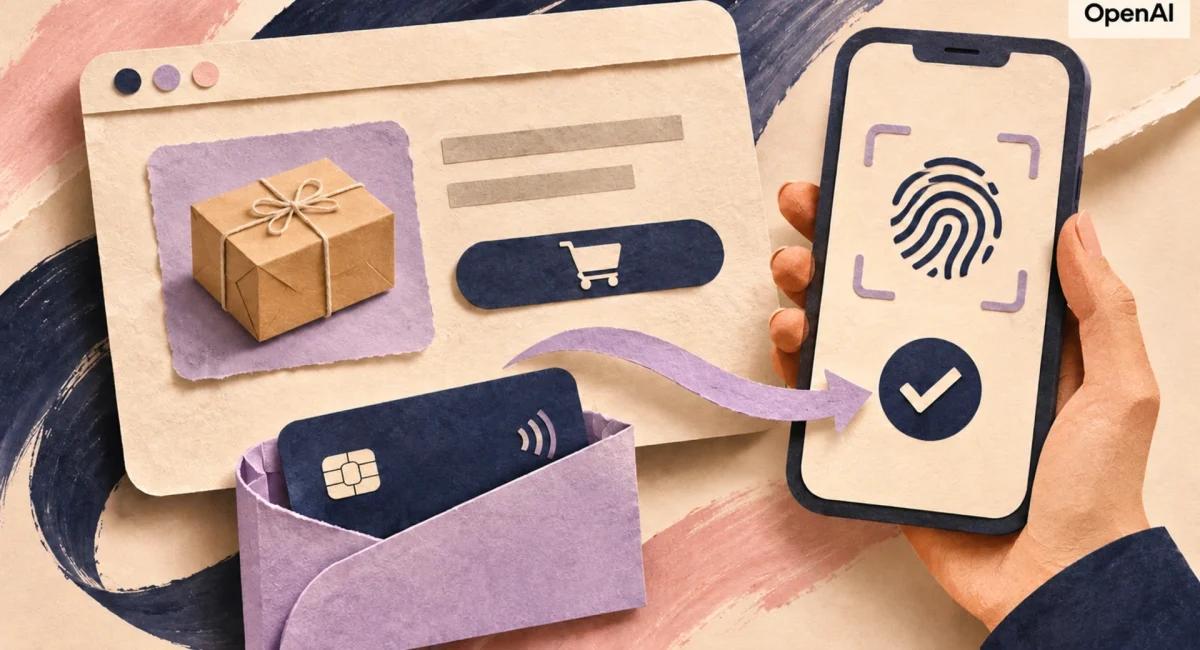
Fraud screening may reject a legitimate order when a customer delegates checkout to a cloud-based agent, as OpenAI’s merchant guidance explains. OpenAI’s November 13 ChatGPT Wallet release puts that incompatibility on a retailer’s technical agenda, alongside its familiar checkout maintenance.
As OpenAI’s announcement explains, the initial rollout reaches ChatGPT Pro subscribers aged 18 or older in the United States, with eligible US-issued cards. Access begins through dots, OpenAI’s personal agents.
Customer Approval Stays Attached to the Purchase
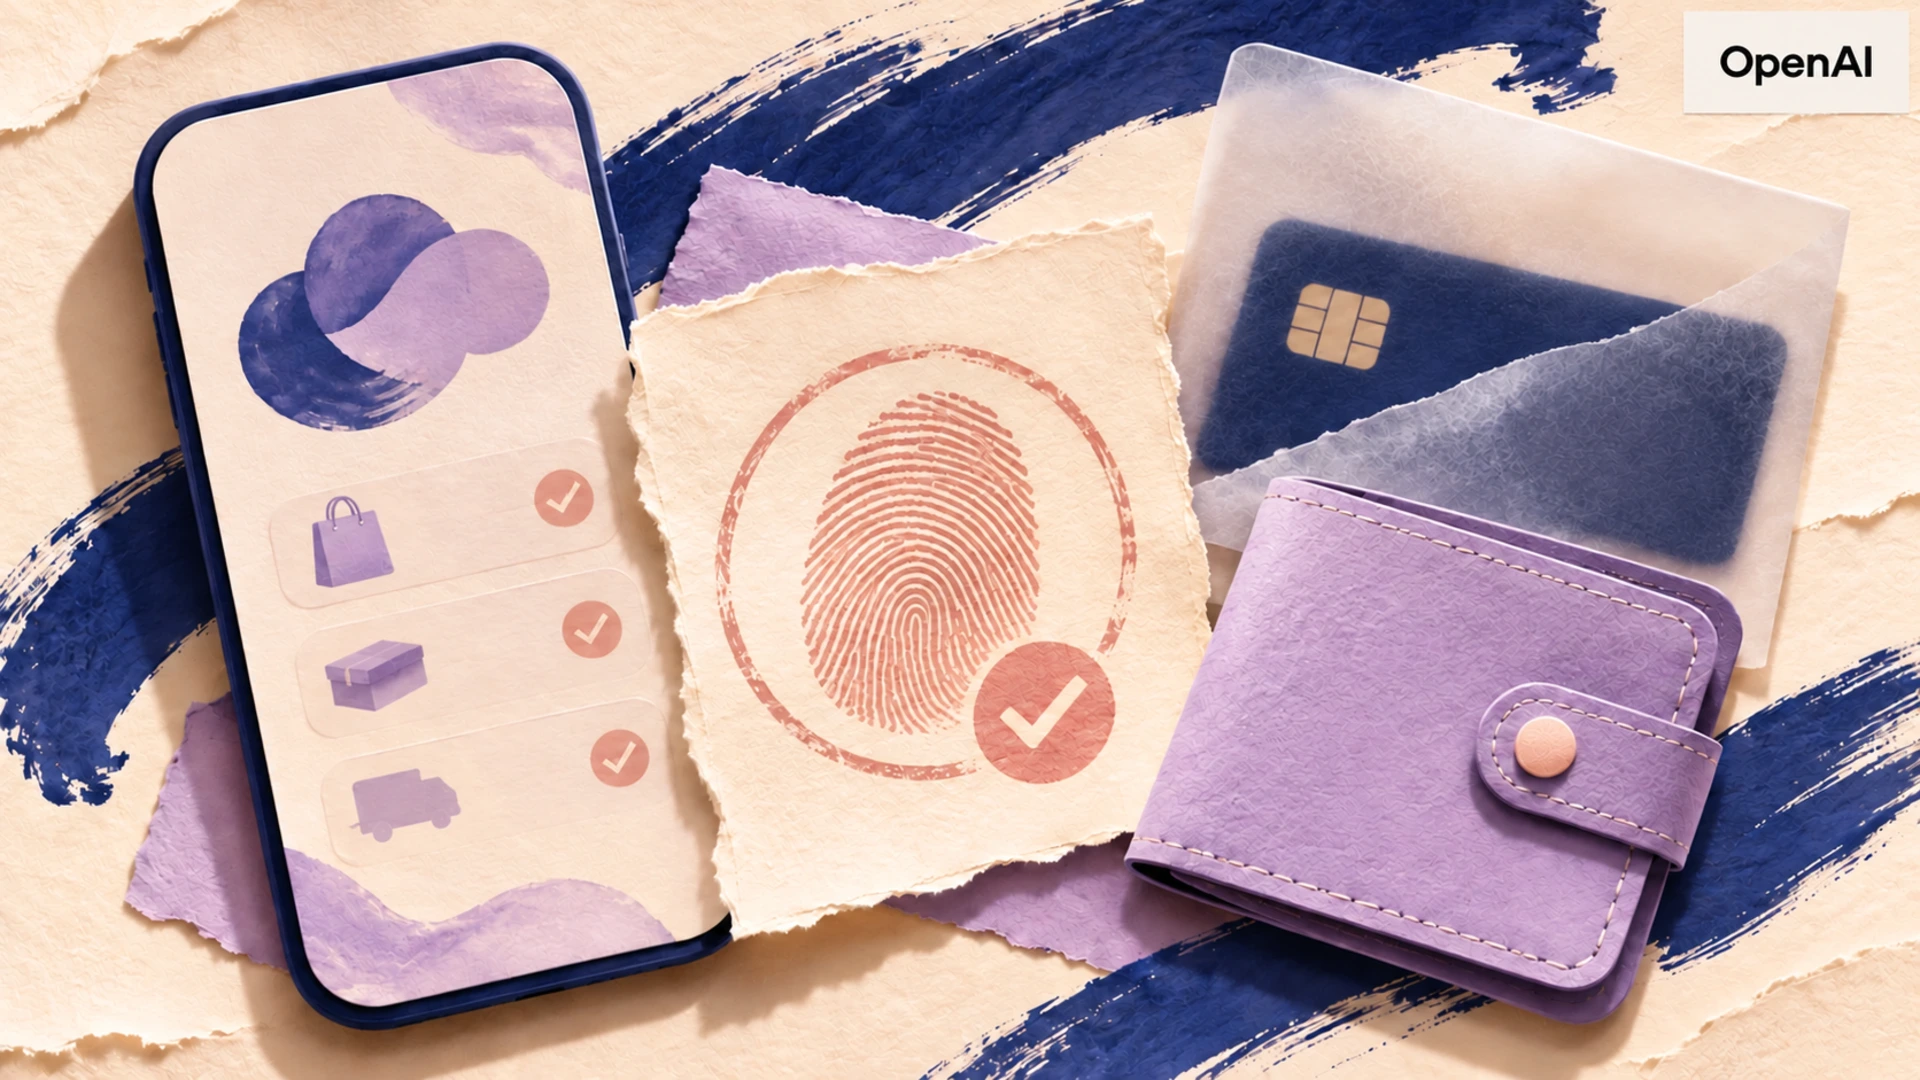
After the customer reviews the purchase total and selected card, approval requires a security check such as a fingerprint scan. Once approval is recorded, payment networks issue substitute credentials for checkout, with actual card details kept separate from the agent and merchant. Card rewards remain available, alongside protections for eligible disputes.
Purchases governed by customer-set limits appear in OpenAI’s future plans, so current checkout tests need to follow today’s per-purchase approval process.
Existing Checkout Infrastructure Remains Relevant
OpenAI’s payment acceptance guide says existing checkout pages already support Wallet’s payment credentials, which makes a custom Wallet integration optional. The merchant processes the order through its checkout and retains responsibility for fraud decisions. Since cloud-browser traffic can trigger systems that evaluate a visitor’s IP address or browser characteristics, payment acceptance still requires examination.
To supply additional context, OpenAI is gradually introducing user signals through the Forwarded HTTP header, with availability varying during rollout. Merchants using external fraud screening need to discuss ingestion with their provider. For internal systems, the guide recommends observing the header. Use those signals within the merchant’s existing risk assessment alongside its other evidence.
Consent applies to the specified transaction, so merchants must treat the resulting payment credential as restricted to that authorized purchase. For subscription purchases, customer consent applies to recurring charges within the existing checkout, subject to processor requirements. OpenAI names Payment Account Reference, or PAR, as the identifier for associating a token with its payment account. Merchants may continue to use their authorized card-on-file purchase flows.
Verify the Browser Traffic You Admit
The agent access documentation describes signed browser requests that a merchant’s security provider can verify, with exceptions needed when current settings block legitimate visits. Cloudflare’s personal-agent settings identify the traffic; Vercel recognizes an existing ChatGPT Agent entry. For both providers, request signatures receive automatic verification. Other configurations require verification against OpenAI’s published authentication material.
For an engineering team evaluating site access, the sensible scope is an exception for verified traffic that preserves existing page-level permissions. Signed browser requests identify a source; the customer’s account still determines access to private order information. Since search crawling has separate rules, a decision concerning a purchasing agent needs its own security review.
For a useful access test, examine where the browser stops and retain the request identifier for investigation with the security provider. When access fails on a product page, the investigation belongs with the team responsible for that page’s security settings. Once the browser reaches checkout, investigate a subsequent payment rejection with the payment provider. Logs need enough detail to connect a customer-authorized test to its failed request, with sensitive payment data excluded from routine diagnostic records.
Product Discovery Needs Current Commercial Data
OpenAI’s product-feed guidance separates discovery data from live purchasing operations, which creates a useful boundary for catalog teams. Via feeds, retailers supply product information for search. When the customer takes action, the merchant’s live website or plugin checks the current offer. Business verification precedes product uploads, and stable item identifiers remain part of the feed requirements.
When a retailer’s stock changes during the day, feed freshness and checkout validation need separate tests that produce their own evidence. Compare the product’s displayed availability against the value returned at purchase time. Check a promotion’s end date too: the offer selected during research may differ from the price available when the customer approves payment. The commerce application needs to communicate the current total at that point.
Catalog accuracy belongs within customer acquisition work as much as software maintenance, since a campaign can attract interest in an offer that the checkout fails to honor. OPERENDIA’s e-commerce development work covers the transaction systems behind those offers. For an agent-access project, an initial engineering brief needs to identify the authoritative inventory source and the application responsible for the final price.
Choose the Integration Work That Your Business Needs
The Commerce Partner Playbook presents browser use and plugins as distinct routes through a customer’s purchase, with different requirements for the merchant’s engineers. Via browser use, the agent follows the existing website. When using a plugin, merchants expose operations that their backend validates when the agent submits a request. ChatGPT selects among available information sources in response to the customer’s request.
Merchants with a working web checkout can use an initial browser test to assess whether additional integration work is justified by observed failures. Measure completion against the task the customer approved. Record the failure location when the attempt stops, then assign the issue to the team responsible for that component. Tie a proposed plugin investment to a named operational problem, such as retrieving location-specific availability through an existing API.
OpenAI’s plugin guidance calls for product lookup that checks the selected offer at the customer’s location, with stable identifiers for the relevant variant. Via cart tools, the merchant returns persistent identifiers and current contents. For supported checkout operations, a browser handoff preserves a route to completion when the plugin needs another action. OpenAI says the interaction between third-party plugins and Wallet remains in development.
Client project estimates require separate acceptance criteria for a browser-based Wallet purchase and a custom plugin checkout that connects to the merchant’s backend. Document the payment route supported by the proposed implementation, then test it against the actual provider behavior. Claims concerning plugin payment compatibility need evidence from the specific integration.
Evaluate the Completed Order
Retailers evaluating agent purchases need an observation period that links a completed checkout to subsequent order handling and any refund requests. Payment authorization supplies only part of the evidence needed for a commercial decision. Track completed orders alongside payment declines, then investigate support contacts associated with the tested flow. Acquisition teams can assess whether the resulting demand justifies further engineering work using their own transaction evidence.
Support preparation deserves a place in that test plan, particularly when an agent communicates success after a delayed response from the merchant. The commerce system’s order record needs to remain the operational reference. To help support staff investigate the actual transaction, customer-facing confirmations should identify the purchased items and the order number. Payment reconciliation then connects the merchant’s order to the processor’s record.
If the customer’s browser receives an uncertain response after submitting an approved order, a retry needs its own test case. Check the existing order status prior to proposing another submission. If the merchant already accepted payment, a second attempt risks another charge. The test record needs to connect the first attempt to its final outcome, so an engineer can distinguish a delayed confirmation from a rejected transaction.
When evaluating development costs, separate the expense required to fix a failed purchase from the expense associated with an additional interface. Assign a named owner to the repair and estimate the effort against the measured failure rate. For an early trial, the merchant’s own evidence is sufficient to decide which defect merits correction; a forecast covering the entire agent-commerce market would add assumptions to that decision.
Businesses selling to eligible US customers have a reason to assess their checkout experience with existing providers and to clearly assign technical ownership. Expansion to other customer groups remains a future product question. Base the next investment decision on observed failures and the cost to correct them.
 Make your brand matter.